The dojo blog.
Vulnerabilities explained with the commands to protect yourself, RouterOS updates to know before installing them, news and products — in English, from official sources.
Image generated locally with ComfyUI from randomly selected elements. How the images are created
MikroTik Safe Mode: How RouterOS’s Safety Net Works
Safe Mode is RouterOS's safety net: while it is active, the router logs every change and, if the session that made them drops, it rolls them back automatically. You enable it with Ctrl+X (or F4) in the terminal and with the Safe Mode button in WinBox. It holds up to 100 actions and does not cover commands that restart the router.
 Knowledge base
The PSD matcher in MikroTik: how RouterOS detects port scans
The PSD matcher in the RouterOS firewall detects port scans: it adds a weight for each different port touched by the same address within a short time window, and when the total reaches the threshold, the rule triggers. Usually, it places the scanner in an address list, and another rule drops it. Place it below the rules that accept legitimate traffic, and note that it does not detect slow scans.
 Knowledge base
MikroTik Firewall Filter: input, forward, output chains and rule order
The RouterOS firewall filter directs every packet into one of three chains: input (to the router), forward (through the router), output (from the router). In each chain, rules are read from top to bottom, and the first match with an action such as accept or drop ends the processing; if no rule matches, the packet passes. For this reason, a new rule must always be placed above the final drop, never below it.
 Knowledge base
MikroTik firewall address list: how they work in RouterOS 7
An address list is a named list of addresses that firewall rules use instead of a manually written address. You add the entries yourself (static) or the firewall adds them automatically as traffic passes (dynamic, usually with an expiration). This mechanism is the basis for blacklists, port knocking, management allowlists, and domain filters.
 Knowledge base
Interface list MikroTik: come funzionano e perché il firewall le preferisce
Una interface list è un gruppo di interfacce con un nome, per esempio WAN o LAN. Le regole del firewall, il neighbor discovery e il MAC server guardano la lista invece della singola porta: quando aggiungi una linea PPPoE, una LTE o una seconda WAN, la metti nella lista e le regole valgono subito anche per lei.
 Knowledge base
MikroTik IP Cloud: How RouterOS Dynamic DNS Works
IP Cloud is the free service that gives your router a fixed DNS name, serial-number.sn.mynetname.net, which follows the public IP address. The router asks the MikroTik server, "What address do you see me at?" and the name points to that answer, even behind a NAT. The name is used to find the router, not to open it.
 Lab
CVE-2018-14847: Recovering plaintext passwords from user.dat on RouterOS v6
We reproduced the CVE-2018-14847 vulnerability on RouterOS v6, confirming that an unauthenticated attacker can read the user.dat file and recover plaintext passwords due to a weak XOR transformation. The issue is fixed in versions 6.40.8, 6.42.11, and 6.49.7, where access to the file is denied.
 Firmware
RouterOS 7.23.8 long-term: fixes and security
MikroTik has released version 7.23.8 of the long-term channel, a conservative release designed for those who prioritize absolute stability. The update fixes a security vulnerability (CVE-2026-84411) and resolves several bugs related to IPsec, OSPF, and storage management. It is advisable to update production devices using the long-term branch after creating a full backup.
 Firmware
RouterOS 6.49.23 long-term: CVE-2026-84411 fix
MikroTik has released version 6.49.23 of the long-term channel for RouterOS 6. The update includes a critical security fix (CVE-2026-84411) and system stability improvements. Installation is recommended on all production devices using the conservative branch, after creating a full backup.
 Dojo
Blocking DNS over HTTPS and DNS over TLS with MikroTik
Encrypted DNS bypasses the router's filter: how to block DoT and DoH on RouterOS 7 using port 853, a name-based address list, the tls-host matcher, and Firefox's canary domain, all tested in the lab.
 Firmware
RouterOS channels: stable, long-term, testing, and development. Which one to choose?
RouterOS is released on four channels: long-term (the most conservative branch, receiving only critical fixes), stable (the recommended current version), testing (release candidates for the next version), and development (beta releases). Use long-term or stable in production; testing and development are for the lab. You select the channel in /system package update; files for all versions, including old ones, are in the [RouterOS Archive](https://mikrotikdojo.com/tools/archivio-routeros/).
 Products
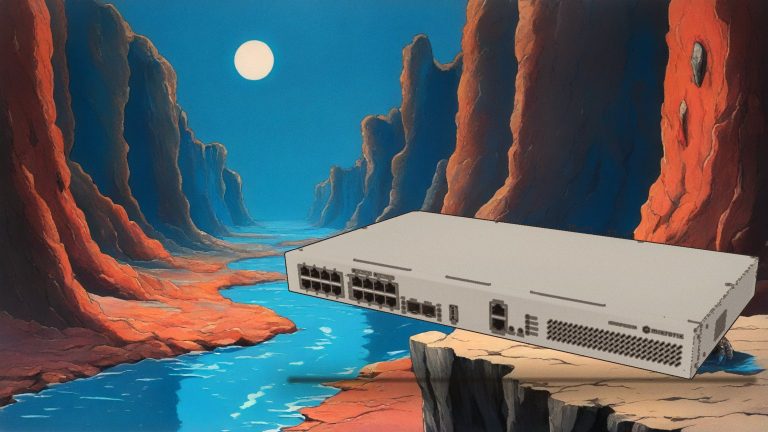
MikroTik CRS418-8P-8G-2S+RM: L3 Switch with PoE and RouterOS
The MikroTik CRS418-8P-8G-2S+RM is a 1U rackmount switch that integrates advanced routing functions, PoE power delivery, and fiber uplinks. It is designed to replace separate routers and switches in small and medium-sized offices, offering centralized network management with RouterOS v7.
 News
LGO-LTE-W: Compact LTE/LoRa Antenna for IoT Installations
The LGO-LTE-W antenna is a compact solution designed for IoT installations where space is limited. It simultaneously supports LTE and LoRa® bands with a gain of 3 dBi. It is the recommended choice for users of the KNOT LR8G/LR9G or KNOT Embedded LTE kits who require a smaller footprint than other options.