The dojo blog.
Vulnerabilities explained with the commands to protect yourself, RouterOS updates to know before installing them, news and products — in English, from official sources.
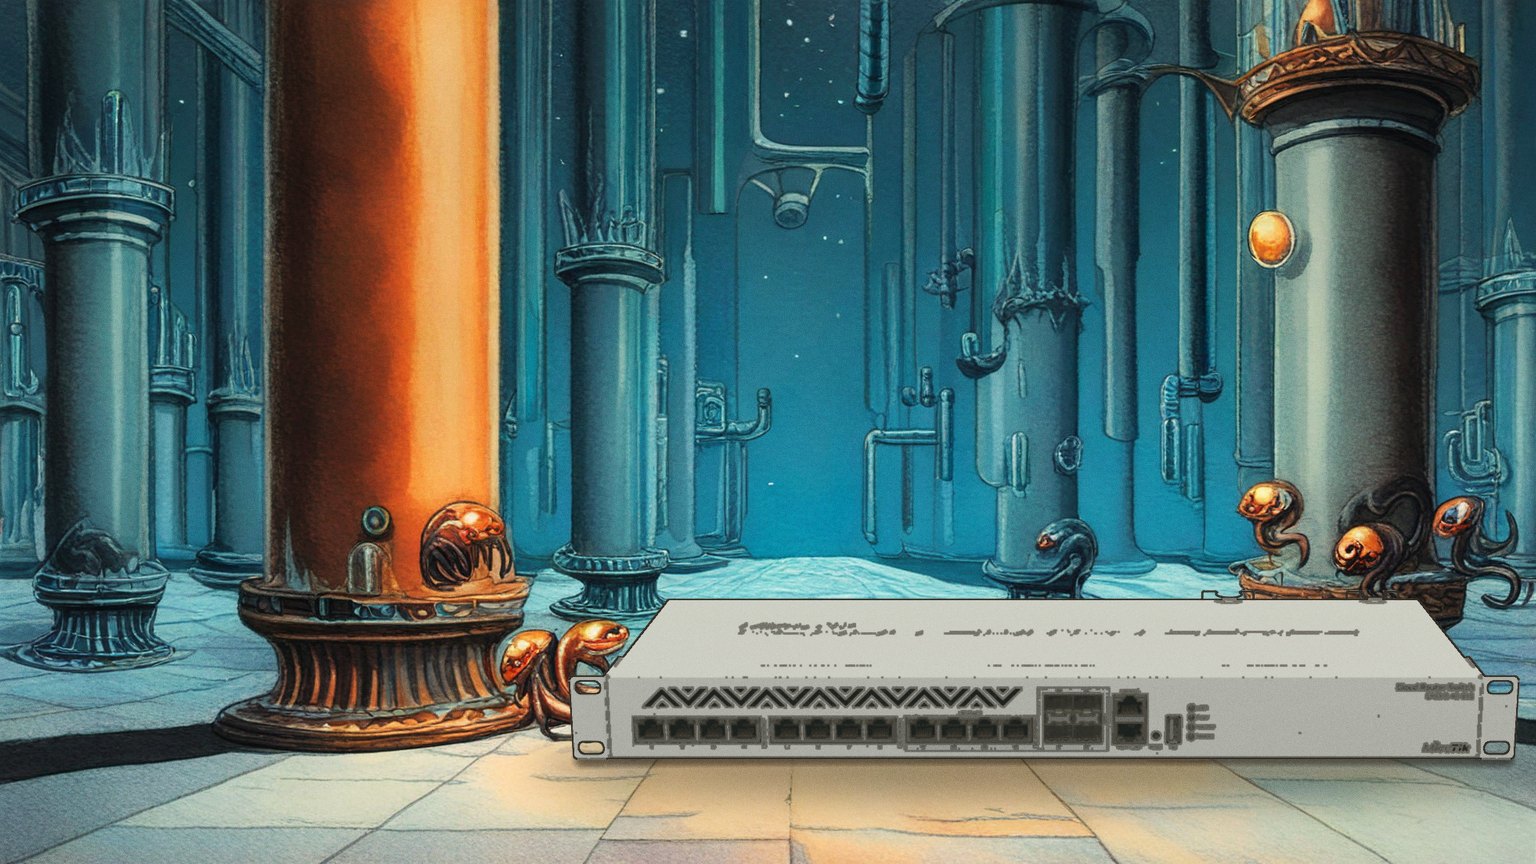
MikroTik CRS312-4C+8XG-RM: 10G RJ45 and SFP+ switch
The MikroTik CRS312-4C+8XG-RM is the first switch in the MikroTik line featuring 10 Gbps Ethernet RJ45 ports. It is designed for professional environments requiring high speed and redundancy, offering a combination of RJ45 and SFP+ ports in a 1U rack format with redundant power.
 Products
CCR2004-1G-12S+2XS: MikroTik Router for SFP and SFP28 Management
The CCR2004-1G-12S+2XS is an enterprise-grade router designed for centralized management of high-speed optical interfaces. It targets WISPs and network administrators who need to aggregate 10G and 25G traffic in a single rackmount device, offering BGP and IPsec processing performance comparable to the CCR1009/CCR1016 models.
 Security
WebFig Exposed in Clear on RouterOS and SwOS
CVE-2025-61481 exposes the WebFig management interface of RouterOS v.7.14.2 and SwOS v.2.18 via unencrypted HTTP, allowing a man-in-the-middle attacker to inject JavaScript into the administrator's browser and intercept credentials. The vulnerability is classified as critical with a CVSS score of 10.0. To mitigate the risk, disable WebFig if not necessary or restrict access exclusively to the trusted management network.
 Dojo
Hotspot and PPPoE MikroTik: the username in every log line
Hotspot connection logs contain IP addresses, not people: to find out who was behind an address, you must cross-reference it with the logins. Using a login and logout script, you can create a log rule for each connected user, with the username in the log-prefix: every log line already contains the name. This works with the hotspot (on-login / on-logout of the user profile) and with PPPoE (on-up / on-down of the PPP profile).
 Security
Buffer overflow in libjson.so of RouterOS 7
CVE-2025-10948 is a buffer overflow vulnerability in the parse_json_element function of the libjson.so component, reachable via the /rest/ip/address/print REST endpoint. It affects RouterOS 7 and can be exploited remotely. Updating to versions 7.20.1 or 7.21beta2 resolves the issue.
 Security
XSS in RouterOS Hotspot
CVE-2025-6563 is a cross-site scripting (XSS) vulnerability in the RouterOS hotspot service in versions prior to 7.19.2. An attacker can inject JavaScript code via the dst parameter to execute scripts in the victim's browser upon login. To mitigate the risk, you must update to version 7.19.2 or later.
 Security
Bypass firewall IPv6 UDP in RouterOS 7
CVE-2023-47310 is a default configuration vulnerability in MikroTik RouterOS 7 that allows IPv6 UDP traceroute packets to bypass the firewall. It affects versions prior to 7.14. The mitigation is to update to RouterOS 7.14 or later.
 Products
MikroTik LtAP LR8 LTE kit: overview and technical specifications
The MikroTik LtAP LR8 LTE kit is a compact all-in-one solution that integrates a 2.4 GHz wireless access point, an LTE Cat 4 modem, a GPS receiver, and a LoRa® gateway in a rugged case. It is designed for remote monitoring, logistics, and IoT scenarios where mobile connectivity, location tracking, and long-range sensor data collection are required without fixed infrastructure.
 Security
VXLAN Vulnerability in RouterOS: CVE-2025-6443
CVE-2025-6443 is an improper access control vulnerability (CWE-284) in the VXLAN service of MikroTik RouterOS that allows a remote attacker, without authentication, to bypass access restrictions and reach internal network resources. Versions 7.15.3 and 7.16.2 are confirmed vulnerable by CVE.org, while NVD indicates all versions prior to 7.20; the exact fixed version has not yet been announced. Those using VXLAN on untrusted networks must update the firmware as soon as it becomes available and verify the service configuration.
 Security
DoS Vulnerability in the SMB Service of RouterOS
CVE-2024-54952 is a memory corruption vulnerability in the SMB service of MikroTik RouterOS 6.40.5 that allows a remote unauthenticated attacker to cause a Denial of Service (DoS) by making the SMB service inaccessible. The version specified as affected is 6.40.5; corrective versions have not yet been announced. To mitigate the risk, you must disable the SMB service if it is not strictly necessary or update to the next stable release when available.
 Security
Account Enumeration in Winbox on RouterOS
CVE-2024-54772 allows an attacker to identify valid usernames on a MikroTik router by analyzing differences in Winbox service response times. Affected versions include long-term 6.43.13 through 6.49.13 and stable 6.43 through 7.17.2. To mitigate the risk, upgrade to version 6.49.18 or later and restrict Winbox access to the management network.
 Products
CRS418-8P-8G-2S+5axQ2axQ-RM: Switch with Wi-Fi 6 and routing
The CRS418-8P-8G-2S+5axQ2axQ-RM is a 1U rackmount switch that integrates a dual-band 4x4 MIMO Wi-Fi 6 controller, 17 Gigabit Ethernet ports (8 of which support PoE-out), and two 10G SFP+ slots. It is designed to replace multiple separate devices in medium-sized offices or server rooms, offering L3 routing capabilities with hardware offloading and advanced management via RouterOS v7.
 Dojo
MikroTik Hotspot: How to Log User Traffic
In a hotspot, users access the internet through a single public IP address: to determine who did what, you need a connection log. With RouterOS 7, this is generated using a firewall rule with action=log applied only to new connections, and sent to an external syslog server, because the router's memory is not an archive. Alternatively, or in addition, you can use Traffic Flow (IPFIX/NetFlow) towards a collector.