The dojo blog.
Vulnerabilities explained with the commands to protect yourself, RouterOS updates to know before installing them, news and products — in English, from official sources.
Denial of Service in the SSH daemon
CVE-2020-10364 is a high-severity vulnerability that allows a remote attacker to cause a denial of service (DoS) on the router, generating excessive CPU activity and potential reboots. It affects systems with the SSH daemon active and reachable from untrusted networks. The primary mitigation is to restrict access to the SSH service to the administration network only or disable it if not required.
 Products
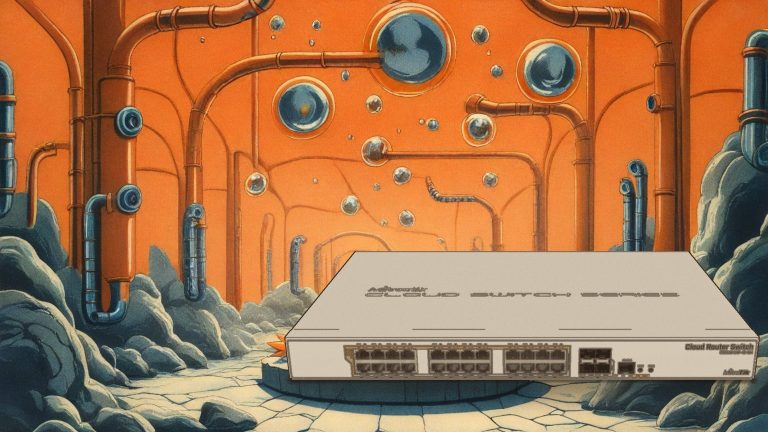
MikroTik CRS328-24P-4S+RM: 1U switch with PoE and Dual Boot
The MikroTik CRS328-24P-4S+RM is a 1U rackmount switch featuring 24 Gigabit Ethernet ports with PoE power delivery and four 10 Gbps SFP+ ports. It is designed for network administrators who require high port density, centralized power for remote devices, and the flexibility to choose between RouterOS and SwOS via the Dual Boot feature.
 Security
Reboot risk from IPv6 packet on RouterOS
CVE-2018-5951 is an availability vulnerability that allows a remote attacker to cause an immediate reboot of a MikroTik RouterOS router. The attack exploits the sending of a specific IPv6 packet with IP protocol 97 (EoIPv6). Since the description states that all RouterOS versions supporting EoIPv6 are vulnerable, it is crucial to verify if this service is active and reachable from untrusted networks.
 Security
Path traversal vulnerability in WinBox
CVE-2020-5720 is a path traversal vulnerability in WinBox, the graphical client for managing MikroTik routers. It affects all WinBox versions prior to 3.21 and allows the creation of arbitrary files if the client connects to a malicious endpoint or suffers a man-in-the-middle attack. To mitigate the risk, you must update WinBox to version 3.21 or higher and restrict access to the service only from the trusted administration network.
 Security
Winbox Vulnerability: Man-in-the-Middle Attack
CVE-2019-3981 is a vulnerability in MikroTik Winbox 3.20 and earlier that allows an attacker positioned between the client and the router to perform an authentication downgrade and retrieve the username and MD5-hashed password. The risk arises when Winbox is reachable from untrusted networks. To mitigate the risk, you must update Winbox to a version later than 3.20 and restrict access to the service to the administration network only.
 Security
DNS cache poisoning vulnerability in RouterOS
CVE-2019-3979 is a high-risk vulnerability that allows a malicious DNS server to poison the router's DNS cache by adding unsolicited A records. It affects RouterOS versions 6.45.6 Stable and earlier, as well as 6.44.5 Long-term and earlier. To mitigate the risk, you must update the firmware or block incoming DNS traffic from the untrusted network.
 Products
CCR2216-1G-12XS-2XQ: 100G core router with L3 offload
The CCR2216-1G-12XS-2XQ is MikroTik's new flagship router, designed to handle 100 Gigabit networks with hardware Layer 3 offloading. It is ideal for WISP operators and data centers requiring high switching and routing capacity, offering a direct upgrade from the CCR1072 thanks to compatibility with existing power supplies and SFP modules.
 Dojo
Wireless scan on a remote MikroTik without losing the result
A frequency scan stops the radio for a few seconds: if you reach the remote router through that wireless link, you lose the connection and the result. The solution is to run the scan in the background on the router itself, saving the result to a file to read once the link is back. In RouterOS 7, this is done with :execute and the file= parameter, which works with both the wifi and wireless packages.
 Security
DNS Cache Poisoning Vulnerability in RouterOS
CVE-2019-3978 allows unauthenticated remote attackers to generate DNS queries toward arbitrary servers, potentially poisoning the router's DNS cache. RouterOS 6.45.6 Stable and earlier, as well as 6.44.5 Long-term and earlier, are affected. You must update the firmware to a later version or block access to the DNS service from untrusted networks.
 Security
RouterOS autoupgrade vulnerability
CVE-2019-3977 allows a remote attacker to force the router to download and install an older version of RouterOS via the autoupgrade function, potentially resetting system credentials. Versions 6.45.6 Stable and earlier, as well as 6.44.5 Long-term and earlier, are affected. You must disable the autoupgrade function or update the firmware to a later version not listed as vulnerable.
 Security
Arbitrary directory creation in RouterOS
CVE-2019-3976 allows an authenticated user to create an arbitrary directory and enable the developer shell by installing a malicious package. It affects RouterOS 6.45.6 Stable and earlier, as well as 6.44.5 Long-term and earlier. The administrator must update the firmware to a version later than those indicated to eliminate the risk.
 Security
Denial of Service in the SMB service of RouterOS x86
CVE-2024-27686 allows a remote attacker to crash the device by sending malicious data packets to the SMB service on TCP port 445. This vulnerability affects RouterOS versions 6.40.5 through 6.49.10 for the x86 architecture. To mitigate the risk, you must disable the SMB service or upgrade to a 7.x version, as the fix is only available in the 7 series.
 Security
Path Traversal Vulnerability in RouterOS (CVE-2019-15055)
CVE-2019-15055 is a path traversal vulnerability that allows authenticated users to delete arbitrary files on MikroTik RouterOS systems. The attack can lead to the reset of credential storage, permitting access to the management interface as an administrator without authentication. You must update the firmware to a version later than the vulnerable releases indicated in the description.