The dojo blog.
Vulnerabilities explained with the commands to protect yourself, RouterOS updates to know before installing them, news and products — in English, from official sources.
Buffer overflow in the RouterOS license update interface
CVE-2018-1156 is an Out-of-bounds Write (CWE-787) vulnerability in RouterOS versions prior to 6.40.9 and 6.42.7. A remote authenticated attacker could theoretically execute arbitrary code on the system through the license update interface. To mitigate the risk, you must update the firmware to the fixed versions.
 Products
CCR2004-16G-2S+: MikroTik router with 16 GbE ports and 2 SFP+
The CCR2004-16G-2S+ is a 1U rackmount MikroTik router designed to deliver high single-core performance at an accessible price. It is ideal for SMBs and WISPs requiring 16 Gigabit Ethernet ports and two 10G SFP+ slots, handling heavy loads based on per-connection processing such as queues. It stands out for its energy efficiency and integrated redundant power supplies.
 Security
WinBox Vulnerability in RouterOS
CVE-2018-14847 is a critical vulnerability in the WinBox component of MikroTik RouterOS that allows an unauthenticated attacker to read arbitrary files and an authenticated attacker to write new ones. The vulnerability is present in RouterOS versions up to and including 6.42 and is listed in the CISA KEV catalog, indicating active exploitation. You must update the firmware to a version later than 6.42 and restrict access to the WinBox service to the management network.
 Security
Denial of Service on the FTP service in RouterOS
CVE-2018-10070 is an Uncontrolled Resource Consumption vulnerability that allows a remote unauthenticated attacker to exhaust the router's CPU and RAM by sending malicious FTP requests. The affected device is MikroTik Version 6.41.4, which reboots after approximately 10 minutes. To protect yourself, you must update the firmware to a later version or disable the FTP service if it is not strictly necessary.
 Dojo
CAPsMAN and WiFi RouterOS 7: enabling client isolation
Client isolation prevents devices connected to the same WiFi network from communicating with each other: in a hotspot or guest network, it is the first defense against people snooping on others' phones. In RouterOS 7, with the new wifi package and its CAPsMAN, it is enabled with client-isolation=yes in the datapath; with the old wireless package, default-forwarding remains, and in CAPsMAN v1, client-to-client-forwarding.
 Security
Buffer overflow in the SMB service of RouterOS
CVE-2018-7445 is a critical vulnerability (CVSS 9.8) in the SMB service of RouterOS that allows an unauthenticated attacker to execute code. It affects all RouterOS versions prior to 6.41.3. The vulnerability is listed in the CISA KEV catalog and requires applying updates according to the vendor's instructions.
 Products
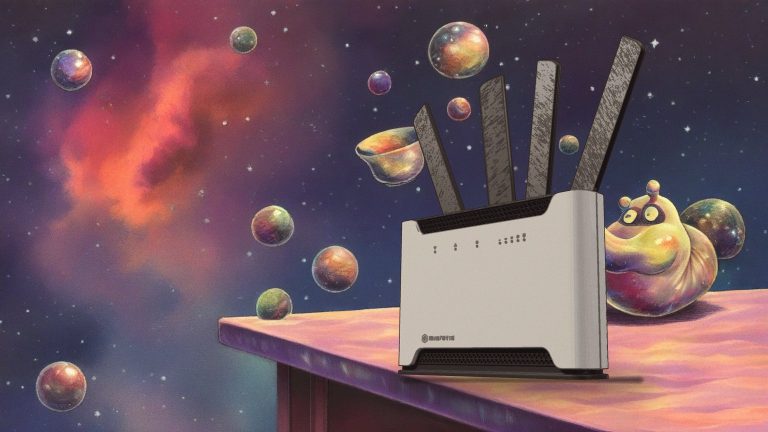
Chateau 5G ax: 5G Router with 2.5G Ethernet and Wi-Fi 6E
The Chateau 5G ax is a 5G/LTE mobile router designed to provide high-speed connectivity with Ethernet ports up to 2.5 Gigabit and Wi-Fi 802.11ax. It is ideal for professionals, WISPs, and advanced users who require flexibility through RouterOS v7 and superior radio performance compared to previous generations.
 Security
Denial of Service via ICMP on RouterOS v6.40.5
The CVE-2017-17538 vulnerability allows a remote attacker to cause a denial of service by sending a massive sequence of ICMP packets. It affects MikroTik devices running RouterOS version 6.40.5. To mitigate the risk, you must update the firmware to a later version or apply network filters to limit ICMP traffic.
 Dojo
How to aggregate multiple internet connections with MikroTik: ECMP and PCC in RouterOS 7
With a MikroTik, you can use two or more internet connections together. ECMP (multiple default routes with the same distance) is the simplest method but does not let you decide which line a connection uses; PCC (Per Connection Classifier) assigns each connection to a line and keeps it there until the end. In RouterOS 7, PCC uses routing tables (/routing table) and gateway checking with check-gateway. We build it in six steps.
 Products
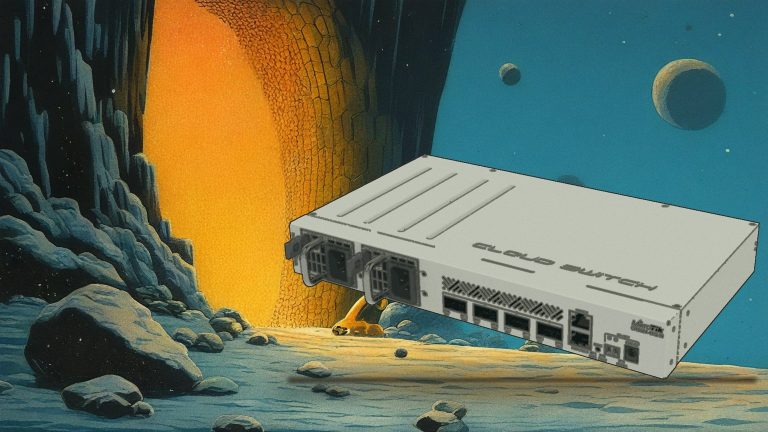
MikroTik CRS504-4XQ-IN: Compact 100G Switch
The MikroTik CRS504-4XQ-IN is a compact network switch with four 100 Gigabit QSFP28 ports, designed to upgrade existing 10 or 25 Gigabit infrastructure. It is ideal for those needing high capacity in limited spaces, thanks to its low power consumption and multiple power options.
 Security
DoS on hAP Lite 6.25 via ACK packets
CVE-2017-6444 is a denial-of-service vulnerability affecting the MikroTik Router hAP Lite device running firmware 6.25. A remote attacker can saturate the CPU by sending unsolicited TCP ACK packets, rendering the router unusable until it is rebooted. Since no fixed versions have been announced, the only certain mitigation is to isolate the device from untrusted networks or replace it.
 Products
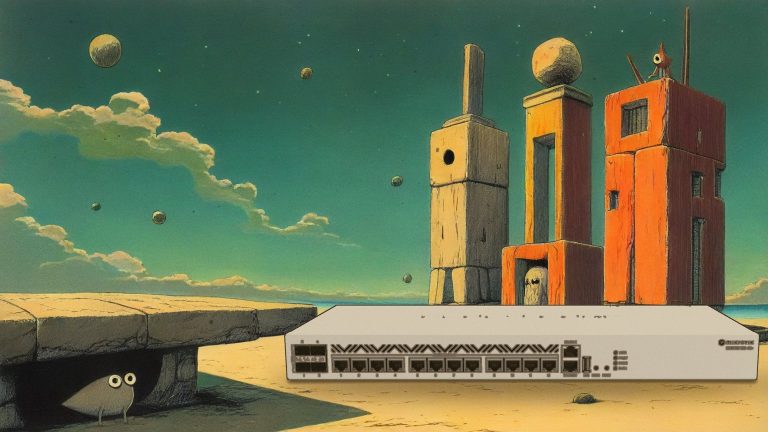
CCR2116-12G-4S+: MikroTik Router with 16-Core ARM CPU and 4 10G Ports
The CCR2116-12G-4S+ is an ISP-grade router based on a 16-core ARM CPU at 2 GHz, designed to eliminate bottlenecks in 10G configurations. It stands out for its high performance in BGP and QoS, powered by typical energy efficiency of only 60 W.
 Dojo
How to reset a MikroTik configuration with RouterOS 7
To reset a MikroTik from the terminal, use the /system reset-configuration command: with no-defaults=yes, the router boots empty instead of with the factory configuration; with run-after-reset, it runs a script immediately after rebooting. If the router no longer responds, use the reset button or, as a last resort, Netinstall.